
Two-Factor Authentication Explained Without the Jargon
Two-factor authentication adds a meaningful layer of protection to your accounts. Here's how it works, why it matters, and the easiest ways to set it up.
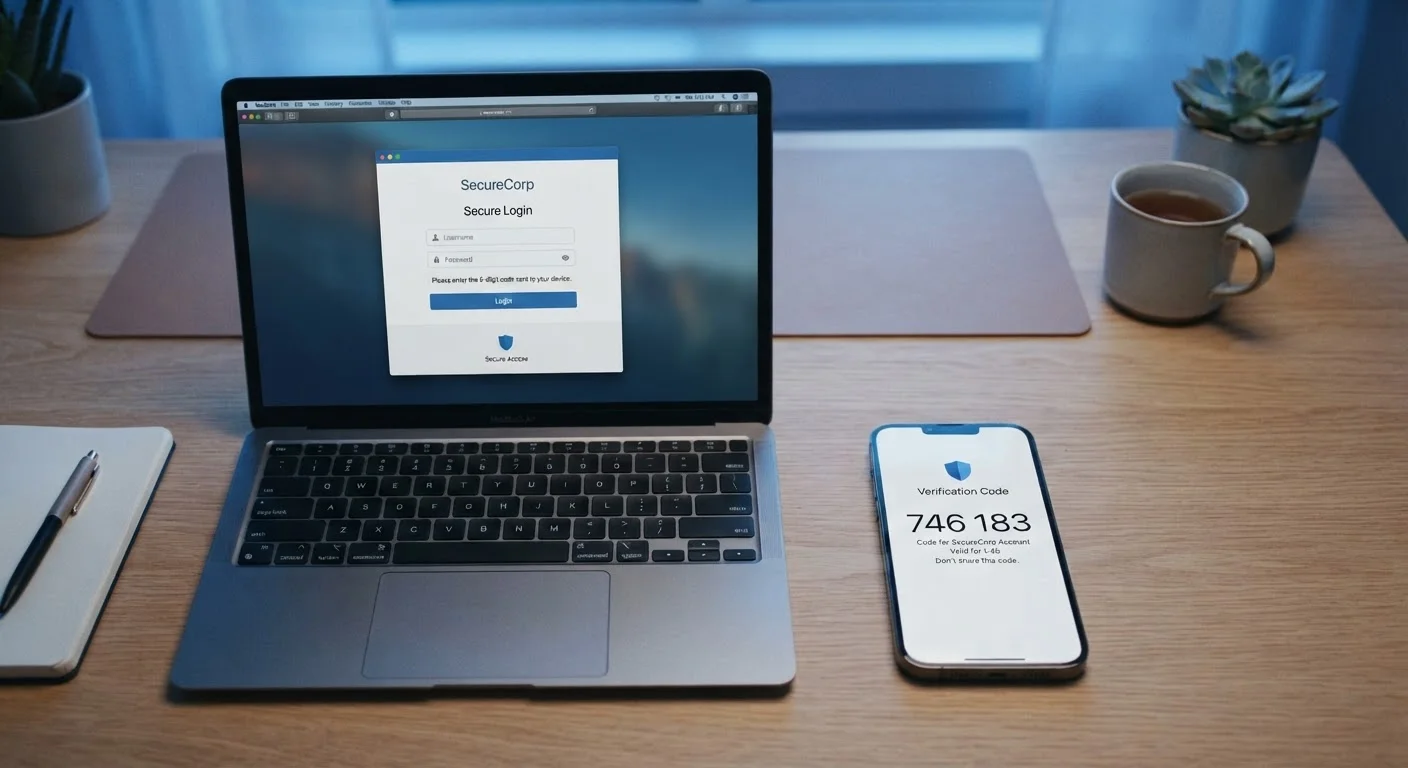
Photo: HorizonMetric.com | One Destination For Everyday Insights editorial
—— In This Article
Key Takeaways
- Two-factor authentication requires a second proof of identity beyond your password alone.
- Even a stolen password cannot unlock your account if the attacker lacks your second factor.
- Text-message codes are common but less secure than authenticator apps or hardware keys.
- Most major services let you enable two-factor authentication in a few minutes inside account settings.
- Prioritize your email, bank, and social media accounts first — those are the highest-value targets.
What Two-Factor Authentication Actually Is
Passwords have one fundamental weakness: anyone who learns yours can walk straight into your account. Two-factor authentication — often shortened to 2FA — plugs that gap by requiring a second, separate proof that you're really you.
Think of it like a bank safe-deposit box. The bank has one key; you hold the other. Neither key alone opens the box. 2FA works the same way: your password is one key, and a temporary code or physical device is the second. A criminal who steals your password still can't get in without that second key.
This matters more than ever. Large-scale data breaches routinely expose millions of email and password combinations. Once those credentials are posted online, automated tools test them against hundreds of other sites within hours. 2FA stops that attack cold, even when your password is already out there. For a broader look at online safety habits, see our everyday internet security guide.
Two-Factor Authentication (2FA)
A login process that requires two separate proofs of identity — typically your password plus a time-sensitive code — before granting account access.
Authenticator App
A smartphone app that generates short, time-sensitive numeric codes used as a second factor during login, without needing a text message or internet connection.
SIM Swapping
A type of fraud where an attacker convinces a phone carrier to transfer your phone number to a SIM card the attacker controls, allowing them to receive your SMS verification codes.
Hardware Security Key
A small physical device — usually plugged into a USB port — that confirms your identity during login without any code you need to type.
Backup Codes
A set of one-time-use codes provided when you set up 2FA, intended to help you regain access to your account if you lose your phone or other second factor.
Phishing
A scam where attackers impersonate a trusted company to trick you into handing over your password or other login details.
The Three Types of Verification
Not all second factors are equal. They fall into three broad categories, each with different trade-offs.
- Something you have — a code delivered to your phone. The most common form. When you log in, a short numeric code is sent by text message or generated by an app on your phone. You enter that code to complete sign-in. Text (SMS) codes are convenient but carry some risk if someone hijacks your phone number. Authenticator apps — standalone apps that generate codes directly on your device — are more secure because no code travels over a phone network that could be intercepted.
- Something you have — a physical key. Small hardware devices that plug into your computer's USB port or tap against your phone. They're the most phishing-resistant option available, though less common and not supported by every service.
- Something you are — biometrics. Fingerprint or face recognition on your phone can serve as a second factor when unlocking an authenticator app or confirming a payment. You're already using this if you unlock your phone with your face.
For most people, an authenticator app hits the right balance of security and convenience. Popular options exist across both iOS and Android — check what your service recommends in its security settings.
Save Your Backup Codes Right Away
When you enable 2FA, the service will typically show you a set of one-time backup codes. Write them down or print them and store them somewhere you won't lose — a fireproof box, a secure notes app, or alongside important documents. If you ever lose access to your phone, these codes may be your only way back in.
How to Turn It On
Enabling 2FA looks slightly different on each platform, but the general path is consistent across almost every major service.
- Open the app or website and navigate to Settings or Account Settings.
- Look for a section called Security, Privacy & Security, or Sign-In Options.
- Find Two-Factor Authentication, Two-Step Verification, or similar wording, and select it.
- Choose your preferred method — authenticator app, text message, or hardware key.
- Follow the on-screen prompts. If you choose an authenticator app, you'll typically scan a QR code (a square barcode) that links the app to your account.
- Save your backup codes in a safe place. These one-time codes let you regain access if you ever lose your phone.
The whole process usually takes under five minutes. Once done, you won't be asked for the second factor every single time — only on new devices or after you log out.
Common Concerns — and Honest Answers
People often delay setting up 2FA because of practical worries. Here are the most common ones, addressed honestly.
"What if I don't have cell service?" Authenticator apps generate codes locally on your device — no internet or cell signal required. SMS codes do require a signal, which is one more reason apps have an edge.
"I'm not tech-savvy enough." If you can send a text message and type a six-digit number, you have all the skill this requires. The setup walkthrough on most platforms is designed for non-technical users.
"My password is already strong." Strong passwords are genuinely important — pairing them with a password manager is a smart move, as security experts explain here. But even a strong, unique password can be exposed in a breach through no fault of your own. 2FA provides protection that a password alone cannot.
2FA Doesn't Make Passwords Irrelevant
Two-factor authentication is an addition to good password habits, not a replacement. Using a unique, strong password for every account — ideally managed with a password manager — combined with 2FA gives you meaningfully better protection than either approach alone. Think of them as working together, not competing.
Which Accounts Deserve It Most
You don't need to enable 2FA on every account you've ever created. Focus first on the ones where a breach would cause the most damage.
- Your inbox is the master key to everything else. Most password-reset links go to email, so whoever controls your inbox can reset passwords across all your other accounts.
- Banking and financial accounts
- Direct access to money. Many banks now require 2FA by default; enable it everywhere it's available.
- Social media accounts
- Compromised social accounts are used to scam your contacts and spread misinformation under your name.
- Work or school accounts
- A breach here can affect colleagues, clients, or sensitive organizational data.
- Cloud storage and backup services
- Photos, documents, and files stored in the cloud can contain sensitive personal information.
Once those high-priority accounts are protected, extend 2FA to any other account that stores payment information or personal data. Understanding how data travels and how it's protected is part of being safer online — reading up on what end-to-end encryption actually means is a natural next step.
Your Service's Security Settings Page
Every major platform — Google, Apple, Facebook, your bank — has a dedicated security or privacy settings section. Search the service name plus 'enable two-factor authentication' to find the exact setup page for each account.
Everyday Internet Security Guide
A broader look at the habits and knowledge that keep everyday Americans safer online, from passwords to privacy settings to spotting scams.
Frequently Asked Questions
Technology Editorial Team
Technology Editorial Team is the collective byline for our editorial team and contributor network. Articles published under this byline or an editorial pen name are researched, written, and reviewed according to our editorial standards for clarity, consistency, and independence before publication.
View author profile