
The Real Difference Between HTTP and HTTPS
That padlock icon in your browser signals something important. Understand what HTTPS actually protects and when it's safe to trust a site.
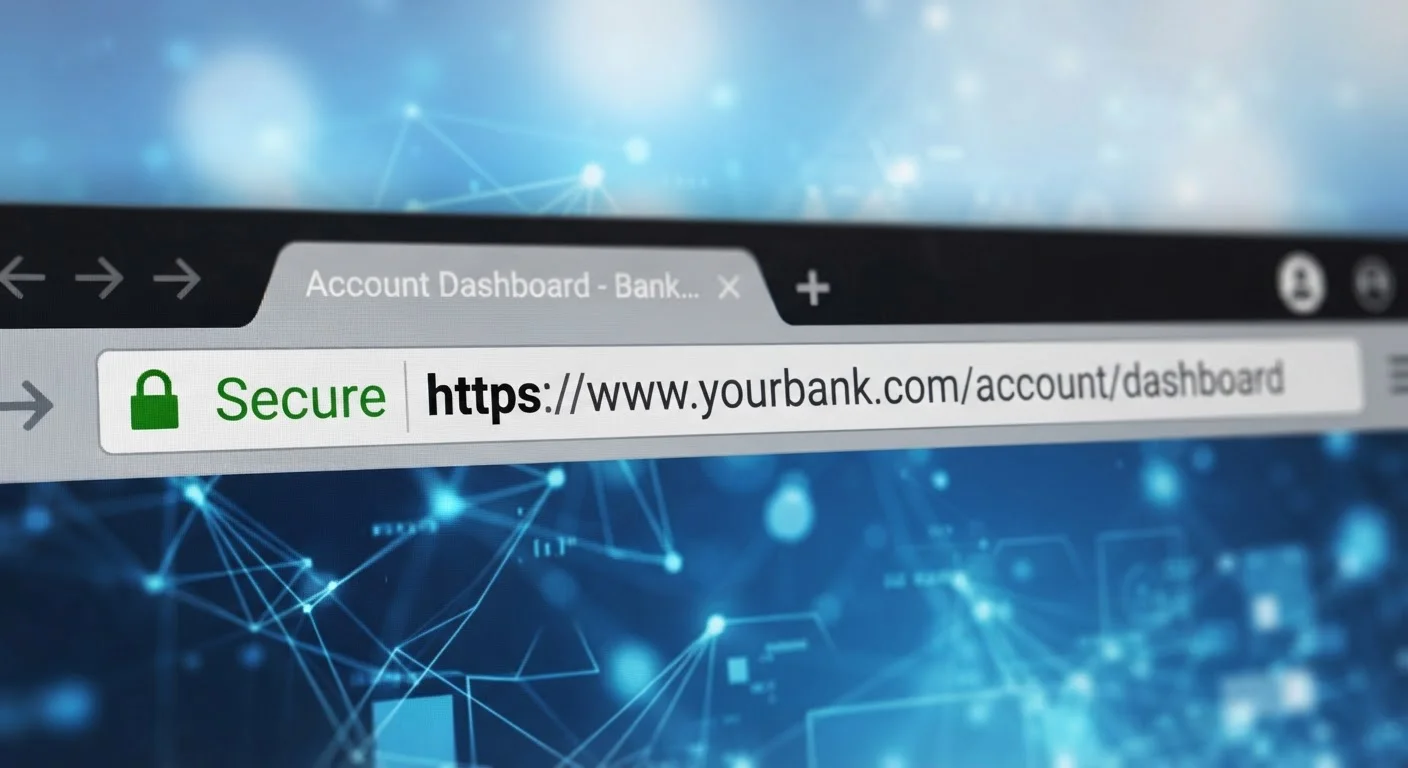
Photo: HorizonMetric.com | One Destination For Everyday Insights editorial
—— In This Article
Key Takeaways
- HTTP sends your data in plain text; anyone intercepting the connection can read it.
- HTTPS encrypts your data in transit, protecting it from eavesdroppers on the network.
- The padlock icon means your connection is encrypted — not that the site itself is trustworthy.
- Scam sites can and do use HTTPS, so the padlock is one signal, not a safety guarantee.
- Using HTTPS matters most when you're logging in, shopping, or entering personal details.
- Most modern browsers now flag HTTP-only sites as 'Not Secure' to alert users.
What HTTP and HTTPS Actually Do
HTTP stands for HyperText Transfer Protocol — the set of rules that governs how data travels between your browser and a website's server. Think of it as the postal system of the web: it determines how information is packaged and delivered.
The problem with plain HTTP is that those packages are sent unsealed. Any router, internet service provider, or bad actor positioned between you and the site can read exactly what you're sending and receiving — including passwords, form entries, and browsing activity.
HTTPS adds one critical layer: encryption. The "S" stands for Secure, and it means the connection uses a technology called TLS (Transport Layer Security) to scramble your data before it travels. Even if someone intercepts the signal, they see only garbled noise rather than readable information.
| Criterion | HTTP | HTTPS |
|---|---|---|
| Data encryption | None — sent in plain text | Yes — encrypted via TLS |
| Padlock in browser | No | Yes |
| Safe for passwords/payments | No | Yes (for transit only) |
| Can be used by scam sites | Yes | Yes |
| Browser warning shown | "Not Secure" label | No warning |
| Protects on public Wi-Fi | No | Significantly better |
What the Padlock Icon Actually Tells You
When you see a padlock in your browser's address bar, it means one specific thing: your connection to that site is encrypted. That's meaningful — but it's not the whole story.
A common misconception is that the padlock means a site is safe, legitimate, or honest. It doesn't. Scammers and phishing sites regularly obtain HTTPS certificates because they're inexpensive or even free to get. The padlock tells you that your data is protected in transit; it says nothing about what the site does with that data once it arrives.
HTTPS Certificates Are Easy to Get
Website owners can obtain a free HTTPS certificate from services like Let's Encrypt in minutes. This is largely good news — it has helped encrypt much of the web. But it also means a fraudulent site can look just as "secure" as a legitimate one. The padlock confirms encryption; it cannot confirm the site owner's intentions or honesty.
So before you trust a site, check two things: the padlock (for encrypted connection) and the domain name (to confirm you're on the site you think you are). A site pretending to be your bank might have a padlock and still be fraudulent. For more on recognizing deceptive sites and messages, see our guide on spotting suspicious emails — the same critical thinking applies to web addresses.
When HTTPS Matters Most — and When HTTP Is Lower Risk
Not every website interaction carries the same stakes. Reading a public news article over HTTP doesn't put your finances at risk. But the calculus changes the moment you start giving information to a site.
HTTPS is non-negotiable when you're:
- Logging into any account (email, banking, social media)
- Entering payment or credit card information
- Filling out forms with your address, Social Security number, or health details
- Using public Wi-Fi — where your connection is far easier to intercept
On public Wi-Fi especially, HTTP traffic is dangerously exposed. Our article on the risks of public Wi-Fi explains why open networks are a favorite tool of bad actors — and HTTPS is one of your key defenses there.
~85%
Web pages loaded over HTTPS
Google's transparency report has tracked a steady rise in HTTPS usage across pages loaded in Chrome, reaching the mid-to-high 80s percentagewise in recent years.
Free
Cost of an HTTPS certificate today
Certificate authorities like Let's Encrypt have made HTTPS certificates freely available, removing a key barrier that once kept smaller sites on HTTP.
For general reading or browsing non-sensitive content on a trusted home network, HTTP carries less practical risk — though major browsers now label HTTP sites as "Not Secure," which is a reasonable nudge to seek out better-secured alternatives.
HTTPS Is One Layer, Not the Whole Shield
Understanding HTTPS helps you make smarter decisions, but it fits inside a larger picture of online safety. Encryption protects your data while it travels — it doesn't protect you from weak passwords, phishing tricks, or account breaches after the fact.
Pairing HTTPS awareness with other habits makes a real difference: using strong, unique passwords (a password manager can help here), enabling two-factor authentication, and understanding what private browsing does and doesn't do all work together. For a broader foundation, our everyday internet security guide covers these habits in one place.
The bottom line: always look for HTTPS when submitting anything personal. Treat the padlock as a necessary check — but never the only one.
Technology Editorial Team
Technology Editorial Team is the collective byline for our editorial team and contributor network. Articles published under this byline or an editorial pen name are researched, written, and reviewed according to our editorial standards for clarity, consistency, and independence before publication.
View author profile